Loading stories…
Inside xSypher // Who we are
Decoding the Future of Technology.
An independent, founder-led engineering publication: software architecture, cybersecurity, AI systems and the hardware developers actually buy — tested, sourced and written by people who build things.
IndependentEngineering & Security Publication
ZeroOutside Investors
100%Editor-Reviewed
100%Transparent & Labelled Partnerships
Our Story & Mission
Why We Built xSypher: Separating Signal From the Noise.
Technology is moving faster than human attention can filter. In an industry flooded with PR hype cycles and synthetic summaries, we champion verified technical truth.
“We don't write for algorithms or venture capitalists. We write for the engineers, security analysts, and curious minds who build and break systems in the real world.”
xS
Anwar Iqbal DawarFounder & Lead Editor
xSypher started in 2025 as a personal notebook about the systems its founder was studying — kernel internals, network protocols, cloud infrastructure and the machine-learning stack — and turned into a publication because the deep material was the part nobody else was writing.
Most technology coverage is written from the press release outwards. That is not a conspiracy, it is an incentive: announcements are cheap to cover and always available. The interesting material sits one layer down — how does this scheduler actually behave under load? What does this advisory mean for a service that already shipped? Is this benchmark reproducible, or was it tuned for the launch? — and that is the layer we work in.
So the standard we hold ourselves to is deliberately unglamorous: read the primary source, run the test, link what you claim, and say plainly when something is unproven. Where we cannot test a claim ourselves, we say whose claim it is. Where we got something wrong, the correction goes on the article.
The name xSypher comes from cipher: a transformation you can specify exactly, verify, and repeat. That is the standard for a technical claim — if you cannot show the procedure, you have not shown anything. The 'x' is the unknown we are still working out, which in engineering is most of it.
Accuracy Over Speed
We would rather be second and thoroughly accurate than first with unverified vendor marketing claims.
Code-Level Audits
Where a claim is testable we reproduce it locally — reference setups, benchmarks and the commands we ran.
Complete Independence
No vendor and no fund sets our verdicts. Where a review unit or a test account was provided, the story says so.
Our Editorial Coverage
The Core Pillars of xSypher
Five areas, one standard: read the primary source, test what can be tested, and link the evidence.
Pillar 01
Artificial Intelligence
Deep technical dives into frontier model architectures, transformer attention mechanics, neural network weight pruning, autonomous agentic loops, and open-weights quantization.
LLMsMulti-ModalLocal Weights
Pillar 02
Prompt Engineering
Treating prompt orchestration as strict systems design. Structured context steering, few-shot reasoning topologies, semantic caching, jailbreak mitigation, and output schema validation.
Context RoutingChain-of-ThoughtJSON Mode
Pillar 03
Cybersecurity & Threat Intel
Offensive and defensive security reporting. Dissecting zero-day CVEs, memory corruption exploits, APT telemetry, Kali Linux methodology, cryptographic breakthroughs, and threat modeling.
Zero-Day CVEsKali LinuxPenetration Testing
Pillar 04
Software Architecture
Full-stack engineering decomposed. Dissecting modern frameworks like Next.js, React Server Components, TypeScript runtime guarantees, high-performance Python backends, and Rust tooling.
Next.js & RSCPython SystemsDistributed DBs
Pillar 05
Next-Gen Gadgets & Silicon
Hardware teardowns, Neural Processing Unit (NPU) benchmarks, edge AI accelerators, RISC-V developments, and hands-on reviews of hardware built for developers and power users.
NPUs & ASICsHardware TeardownsEdge Compute
Original reporting
Long-form reporting
Longer-form reporting on security incidents, supply-chain failures, regulatory pressure, and the engineering decisions inside products people actually use.
The Team
Who builds xSypher
A small, founder-led team of engineers and researchers. Everyone here writes, tests and ships — there is no layer of management between a story and publication.
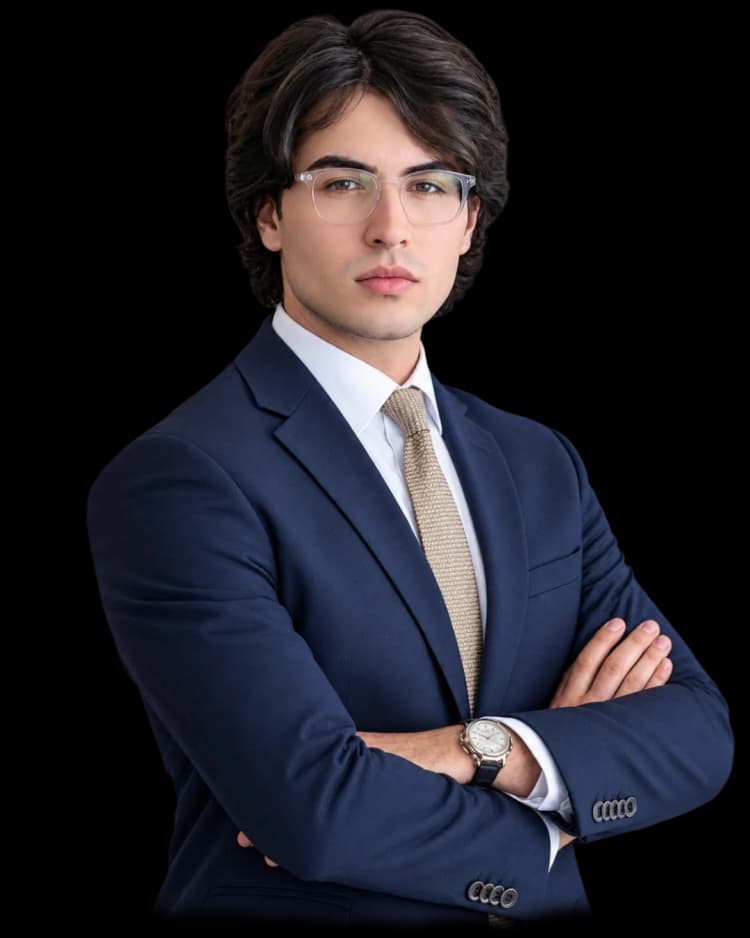
Biography & Technical Stance
Anwar Iqbal Dawar built his foundational expertise while pursuing a BS in Computer Engineering at CECOS University Peshawar. Driven by an intense curiosity for how complex networks and software systems operate at a hardware level, Anwar focuses on identifying structural vulnerabilities before they can be exploited. His engineering background provides a rigorous, math-and-logic-driven approach to solving modern security challenges.
Looking ahead, Anwar is actively shaping his trajectory toward an MS in Cybersecurity, with the ultimate goal of becoming a Cyber Cloud Engineer. He believes the future of technology lies in securing decentralized, cloud-native infrastructures. At xSypher, Anwar ensures that every piece of technical journalism is grounded in authentic engineering principles, bridging the gap between academic research and frontline cloud defense.
Core Specializations & Tools:
C++ & PythonFull-Stack Web DevelopmentNext.js & React ArchitectureLinux OS AdministrationCloud Infrastructure SecurityPenetration Testing
Co-Founder & CTO
Ameer Muawiya Khattak
Engineering & Infrastructure
Builds and maintains the platform this publication runs on — the web application, the database and storage plumbing, and the deployment pipeline — alongside his own infrastructure work.
Systems & Security Engineer
Tariq Jameel
Computer Engineer • Cyber Infrastructure
Computer Engineer focused on cyber defense, networking protocols, and Linux system administration. Adept in Python automation and modern web development architecture.
Lead Security Researcher
Khizar Muzzamail
Vulnerability Research & Audits
Researches and writes on vulnerability analysis, attack-surface review and defensive tooling — including the parts of a disclosure that a vendor advisory tends to leave out.
Ethical Standards
What we promise — and what you can hold us to
Four commitments that decide what runs, what gets corrected, and who gets a say in it.
1. Primary-source verification
We do not pass on vendor claims as findings. Technical statements, performance numbers and vulnerability reports are checked against the primary source — the specification, the repository, the advisory — and tested on our own machines wherever a test is possible. When a number came from somebody else, the story says whose it is.
2. A real wall between editorial and commercial
No advertiser, sponsor or investor gets preview access or a say in what we publish. The publication is supported by clearly labelled Sponsored Deep-Dives, Partner Content and display/newsletter sponsorships — every paid format carries a “Sponsored” or “Partner” tag before the first paragraph. Where a sponsor's product is independently reviewed, the verdict stays ours: sponsorship buys placement, never conclusions.
3. Corrections live on the article
When we get something wrong, the fix goes on the story itself, with a timestamp and a note explaining what changed. Minor typos are fixed silently; substantive changes never are. Anyone can report an error and get an answer within two business days — the policy and the form are on our corrections page.
4. Source protection, honestly described
Sensitive tip? Ask for an encrypted channel and we will use one — authors can publish a PGP key on their profile. We keep the minimum material needed to verify a story and publish nothing that could identify a source who asked us not to. We will also tell you plainly what we can and cannot protect: we do not operate a third-party secure-drop service, and we would rather say that than pretend otherwise.
Connect with xSypher
Got a tip, a correction or a system worth tearing down?
We read every credible tip, technical correction and collaboration request ourselves. If something here does not match how we behave, tell us — that is the fastest way to get it fixed.